מאמרים מאת יוסי שביט #OT ASSTETS
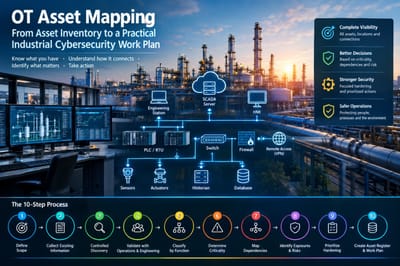
One of the fundamental prerequisites for protecting industrial control systems is the ability to answer a seemingly simple question: What is actually connected to the industrial network? In many industrial facilities, there is no complete and up-to-date picture of all assets. Alongside SCADA servers and engineering stations, there are PLCs, HMIs, sensors, actuators, switches, communication converters, Safety systems, supplier laptops, communication equipment, and sometimes legacy components that are no longer properly documented. In the IT world, it is often possible to perform active network scans and automatically identify assets. In OT environments, however, a more cautious approach is required. Uncontrolled scanning can potentially affect a controller, network device, or even a physical industrial process. Therefore, OT asset mapping must be an engineering, operational, and cybersecurity process, not merely a technical activity. The goal is not simply to create a list of assets, but to establish a basis for decision-making: which assets are more critical, which are more exposed, what dependencies exist between assets, and what should be hardened first
קרא עוד

